2026 CDO Report: Meet the Modern Data Team New survey of VP & C-level data and AI leaders confirms what’s stalling AI transformation.
What Is a Chief Data Officer in 2026? Many people working within the data industry are saying the same thing: the role of the Chief Data Officer (CDO) has changed – but how? CDO Magazine began an expert survey to find out. We recent...
The 6-Layer Operational Framework for Enterprise AI Agility What does AI agility mean? AI agility refers to how fast an AI system—and the organization behind it—can adapt to shifting data and market conditions. AI agility is all about speed and adaptability. I...
US Federal News Bureau
Pentagon Data Breach Highlights Gaps in Sensitive Data Governance

Written by: Tathagata Sen
Updated 2:32 AM EDT, October 6, 2026
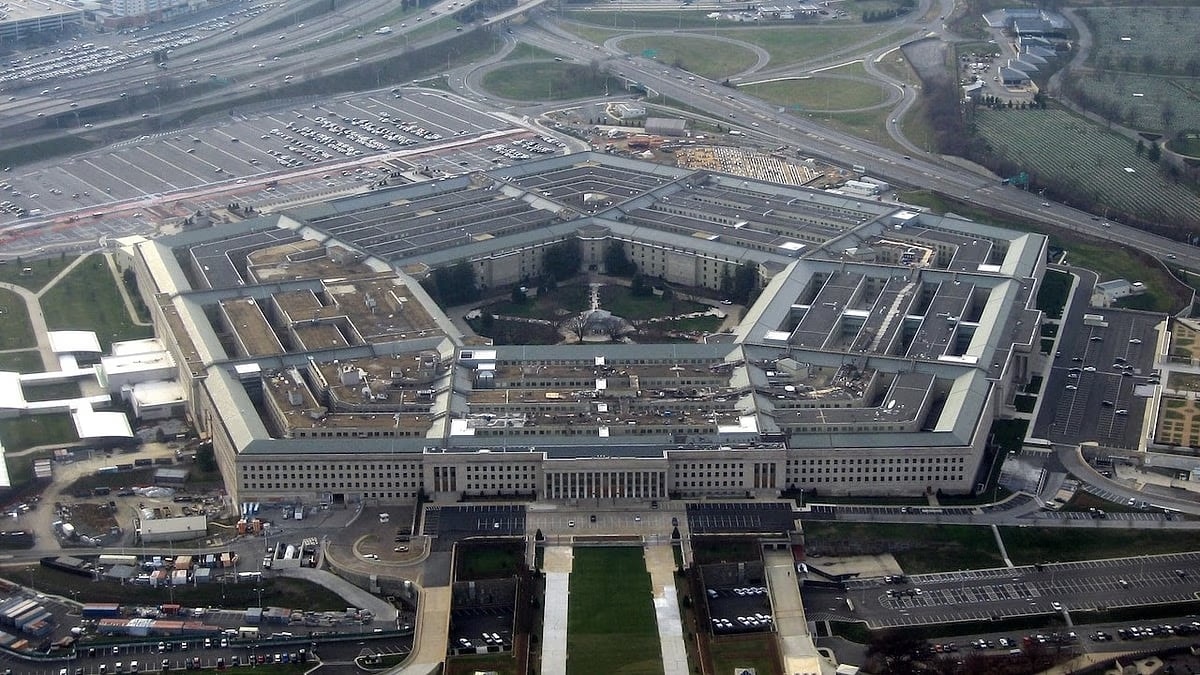
Unauthorized users accessed sensitive personnel records at the Pentagon’s Defense Manpower Data Center (DMDC), affecting about 3 million people, Nextgov reported October 5.
The breach, which took place between October 2025 and July 2026, went undetected for roughly nine months. The records accessed included names, Social Security numbers, birth dates and other personnel details across the military and other government, which DMDC manages.
A vulnerability in DMDC’s file-sharing system allowed users to access the sensitive information, according to Nextgov. The incident highlights the challenge of maintaining visibility over sensitive data, controlling access and detecting unauthorized activity.
Sensitive Data Needs Continuous Oversight
For chief data officers (CDOs), the incident highlights the importance of clear ownership over sensitive datasets. Organizations also need visibility into where sensitive data resides, how it moves between systems and who can access it.
Sensitive data requires stronger safeguards, particularly when it is stored in shared or legacy systems. Clear responsibilities are also important when a breach occurs, with defined ownership for detecting, containing and reporting incidents involving sensitive data.
Strong data-management processes can help establish that ownership and maintain visibility over sensitive information throughout its lifecycle.
 Elevate Your Personal Brand


