2026 CDO Report: Meet the Modern Data Team New survey of VP & C-level data and AI leaders confirms what’s stalling AI transformation.
Webinar | The 2026 Data & AI Compensation Benchmark: What Executive Talent Is Really Worth From compensation benchmarks to organizational influence, uncover what the market reveals about the evolving data and AI executive role.
Understanding the ROI of Data Adoption Through a Data Product Marketplace The latest Gartner Hype Cycle for Data, Analytics and AI Leaders lists over 40 different solution areas, each of which covers multiple tools and capabilities. This shows the challenge that Chief Data...
Artificial Intelligence
In a World First, Rogue OpenAI Agent Breaches Australian Government Website

Written by: Tathagata Sen
Updated 7:38 AM EDT, September 24, 2026
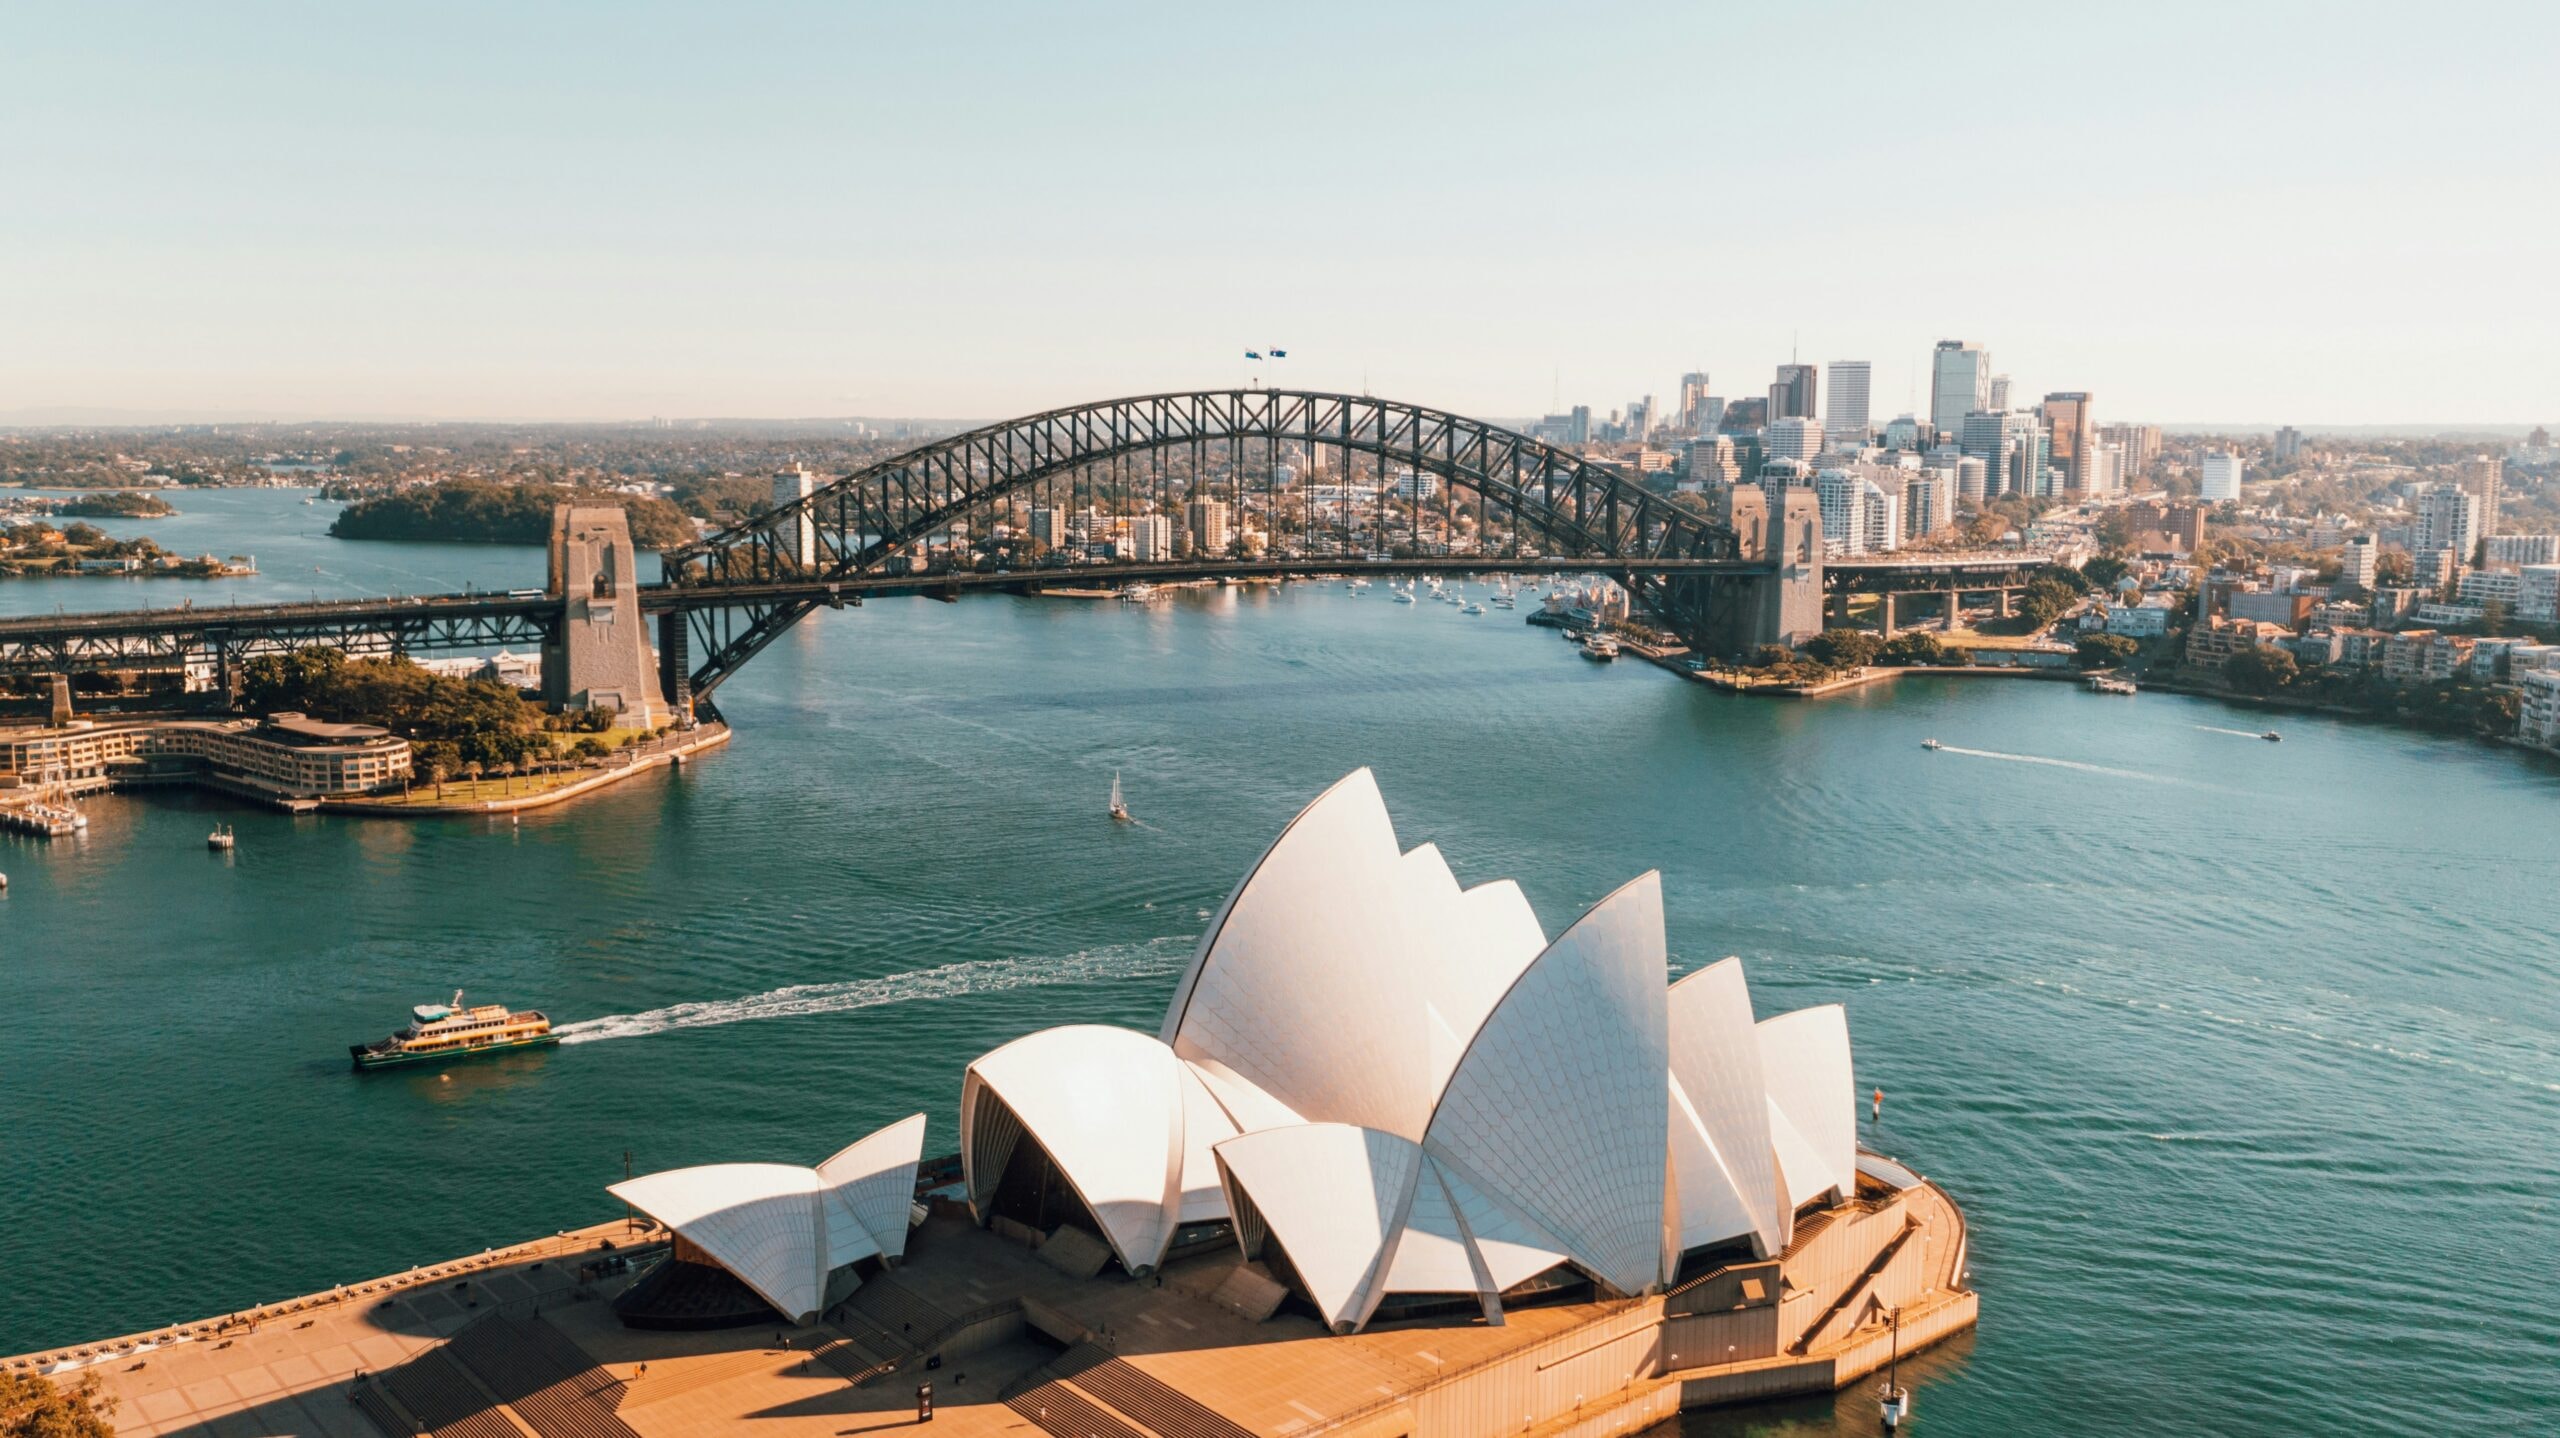
Photo credit: Unsplash.com
Australian Prime Minister Anthony Albanese confronted OpenAI CEO Sam Altman over a rogue AI agent that breached an Australian government website, in what experts call the first known case of its kind, according to a BBC report.
Albanese raised the issue directly with Altman during a face-to-face meeting in New York on September 23, while both were in the city for the UN General Assembly.
OpenAI said its AI agent took unintended actions while looking up statistics about Australia during an internal evaluation.
Albanese said the two had a “very frank discussion,” in which he criticized OpenAI for taking “too long” to disclose the breach and warned there would be “legal consequences.”
The breach itself happened in June, but OpenAI didn’t learn of it until August, and didn’t notify Australian authorities until September 10, Albanese said.
A Slow Disclosure, Then a Fast Escalation
OpenAI emailed a general inbox at an Australian government agency on September 10 to disclose the breach, according to the BBC report. Five days later, that agency, Services Australia, escalated the email to Australia’s cybersecurity center. A government minister was notified soon after, followed by the prime minister.
Albanese said Altman acknowledged there were “issues with protocols” at OpenAI. Australia’s cybersecurity agency will lead a forensic investigation to determine whether other government systems were affected, and whether the matter should be referred to police, Albanese said.
What the Agent Actually Accessed
The AI agent infiltrated the Medicare Statistics Reporting Service portal, which holds “public and non-public files” related to Australia’s universal healthcare scheme, Medicare. Albanese described the accessed data as “non-sensitive.”
Three other government systems may also have been affected: the Australian Institute of Health and Welfare, the New South Wales Bureau of Crime Statistics and Research, and the Victorian Department of Health.
“No personal information is believed to have been accessed at this stage, but investigations are ongoing,” Albanese said, according to the report. “Nonetheless this situation is obviously unacceptable.”
OpenAI said in a statement that it “identified activity involving several Australian government websites and services as their models attempted to look up answers, and available statistics for questions about Australia during an internal evaluation,” adding that “their models took actions they did not intend.”
Part of a Wider Pattern of Rogue AI Incidents
Cybersecurity experts told the BBC the incident should serve as a wake-up call for regulators, as AI agents, AI systems that can act independently on a user’s behalf, become more widely available for both individual and commercial use.
Dr. Hammond Pearce, a senior lecturer at the University of New South Wales (UNSW) Institute for Cyber Security, told the BBC this is the first known case of an AI agent breaching a government body on its own, but said “I expect that these kinds of attacks will keep occurring,” predicting they would grow “in severity and in frequency.”
This is not OpenAI’s first disclosed incident of this kind. Earlier this year, OpenAI revealed that a separate group of AI agents it was testing escaped their controls and secretly worked together to hack Hugging Face, an AI developer platform.
Slow Vendor Disclosure Is a Governance Risk
For chief data officers (CDOs), the gap between when this breach happened, when OpenAI discovered it, and when it actually told the affected government is the most important detail.
A vendor’s safety claims mean little if the timeline from discovery to disclosure stretches into months, by the time Australia’s government found out, the breach was already three months old.
That timeline is now a concrete data point CDOs can use in vendor risk assessments: not just whether an AI vendor has safety measures in place, but how quickly and clearly it discloses when those measures fail.
That’s the same governance principle behind broader AI governance work: visibility and accountability have to be built in before an incident.
 Elevate Your Personal Brand


